Red04
An end-to-end encrypted messenger for iOS and Android. Private keys stay locked inside the phone's security chip, and the server only relays sealed messages — it never holds content or keys.
 Red04
The problem
Ordinary chat apps keep readable history on a server and let keys travel with backups, so one breach or one copied backup can expose a whole conversation.
Our answer
Red04 encrypts every message on the device with a key that cannot leave the phone's Secure Enclave or StrongBox. A relay server routes sealed envelopes and holds them for offline recipients for at most seven days; the history itself lives only on members' devices.
A quick look at Red04
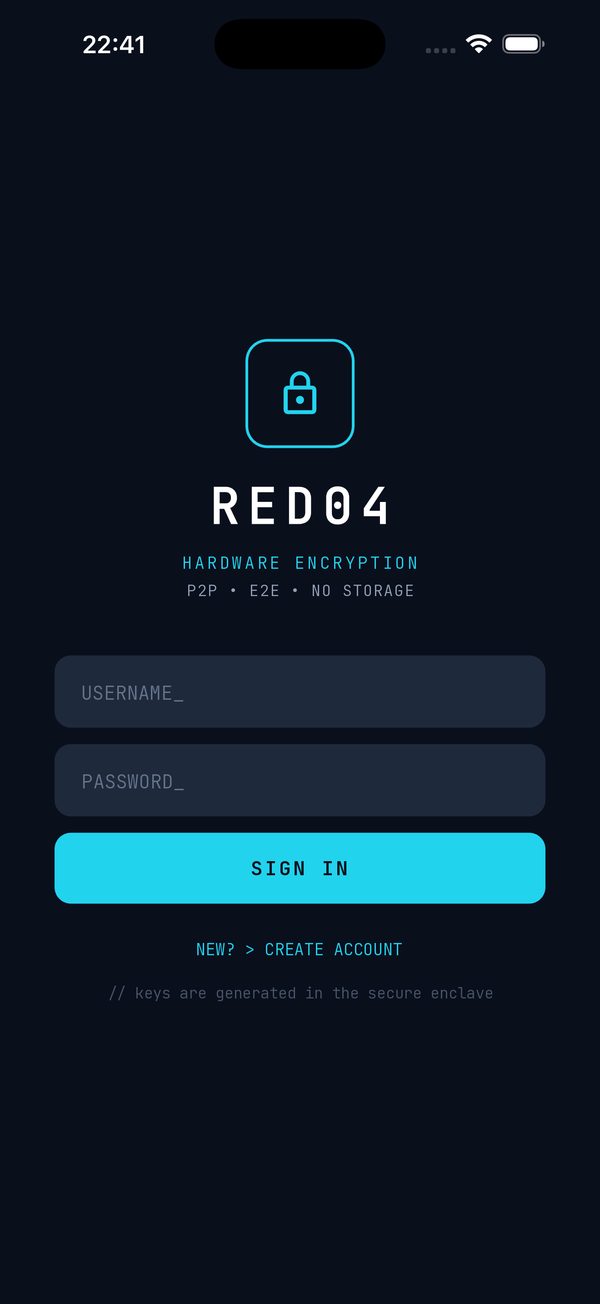
Sign-in
An account is tied to a key generated inside the phone's security chip the first time it signs in.
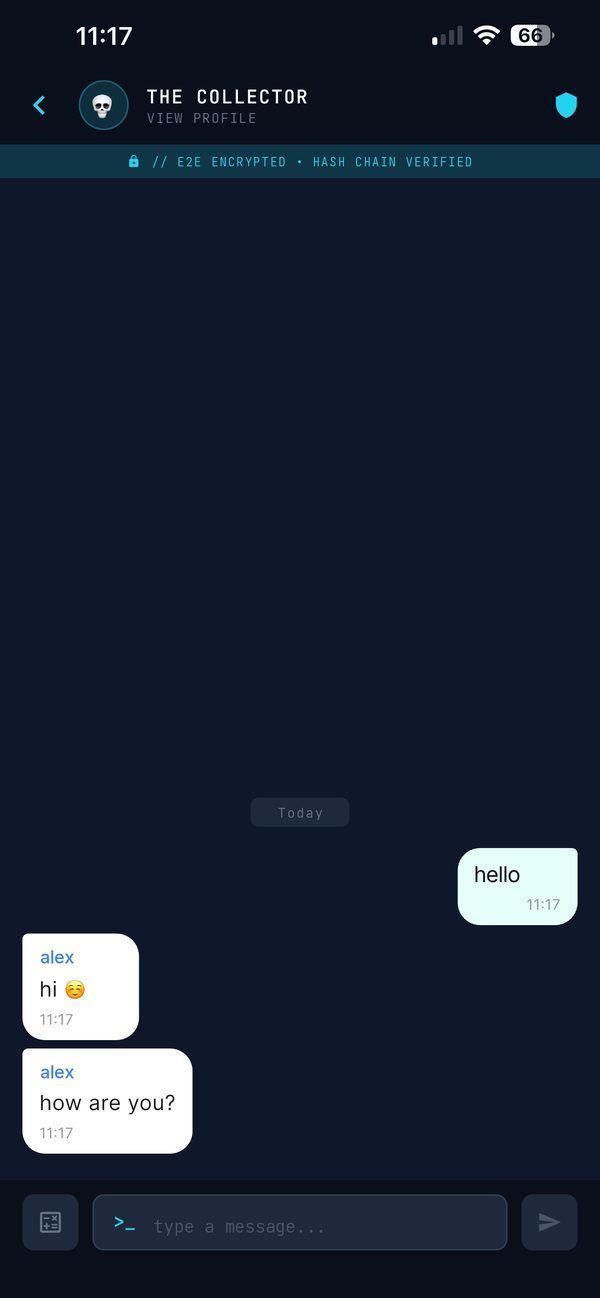
Encrypted chat
Each conversation shows its end-to-end status and whether the hash chain has been verified.
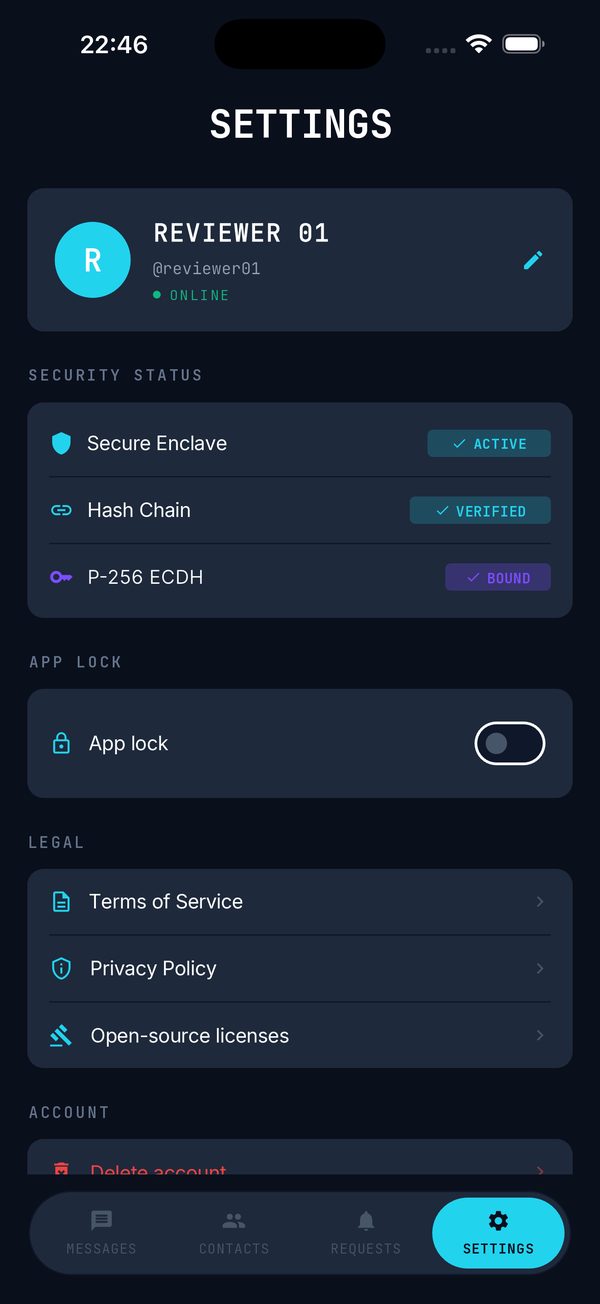
Security status
Secure zone, hash chain and key binding at a glance, with app lock one switch away.
What it does
- Hardware-bound keys — private keys are generated inside Secure Enclave or StrongBox and cannot be exported; the app only holds a handle.
- Relay-only server — no message content, keys or history on the server — history stays on members' devices and syncs between them.
- Tamper-evident messages — a per-sender SHA-256 hash chain flags any altered message; messages cannot be edited, deleted or recalled.
- Groups run by vote — adding a member needs every member's approval — plus app lock with PIN or biometrics and optional secure wipe.
Have an idea? Let's make it real.
Tell us the problem you are trying to solve — a proposed solution and roadmap within 48 hours.
Start a project